We identify vulnerabilities before they become real security risks.
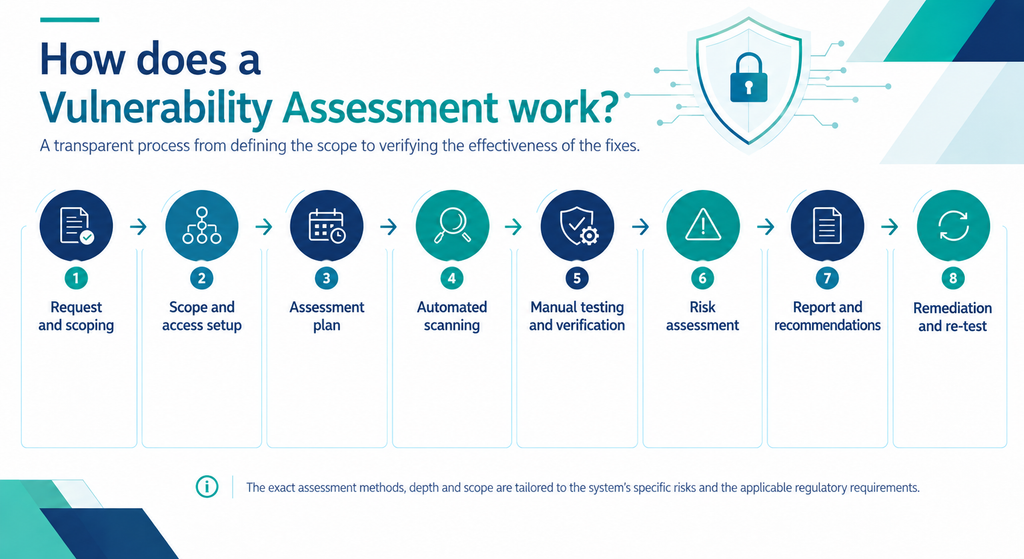
The purpose of vulnerability assessment is to identify security weaknesses in electronic information systems, applications, and infrastructure, and to evaluate the risks associated with the vulnerabilities discovered. The outcome of the assessment is a professional report that clearly presents the identified issues, their significance, and the recommended remediation measures. Under the applicable regulatory framework, a vulnerability assessment is not an official regulatory inspection or audit, but a technical assessment aimed at strengthening the protection and security of IT systems.
OnA Assessment Body Ltd. is listed in the current register of organizations authorized by the Supervisory Authority for Regulatory Affairs (SZTFH) to perform vulnerability assessments, and is therefore entitled to provide such services as an authorized business entity.
What do we assess?
The scope and content of each assessment are tailored to the system concerned, its specific risks, and the defined scope of the engagement. For comprehensive vulnerability assessments, the applicable legislation identifies, among other areas, external and internal IT security testing, application security testing, wireless network assessments, and the assessment of cyber-physical systems. Additional methods may include automated vulnerability scanning, penetration testing, cryptographic compliance testing, and source code review.
Assessments may be carried out without authentication, with registered user access, or – where justified – with administrator-level access. This enables us to evaluate the system from different attacker and user perspectives.